Secure. Compliant. Audit Ready.
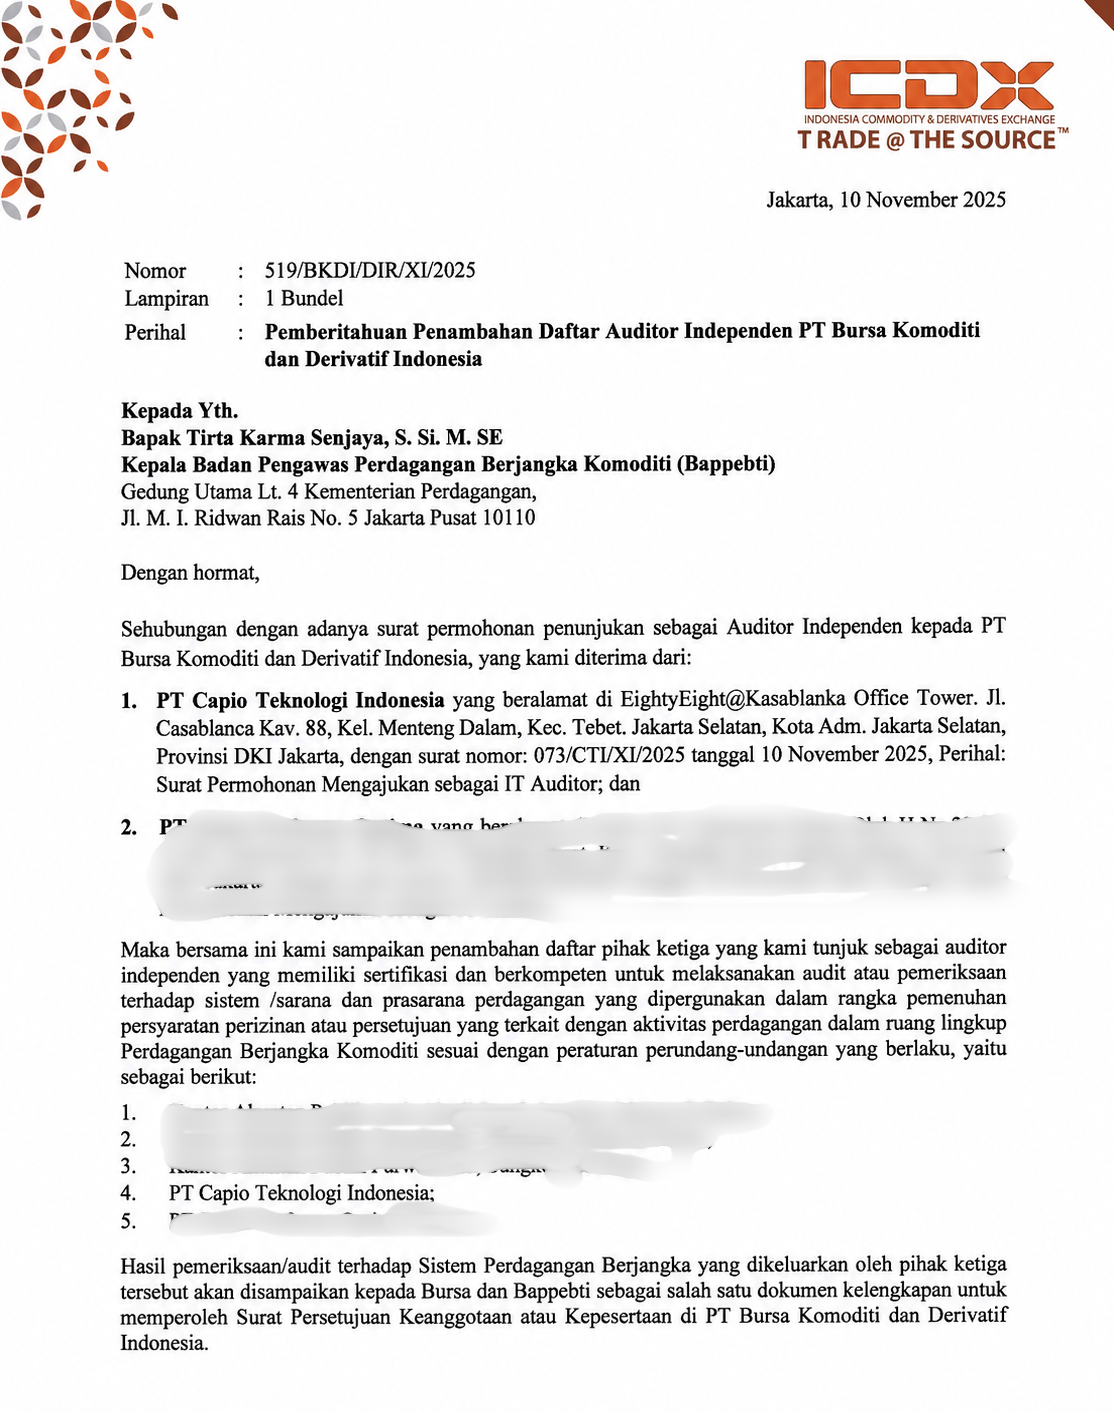
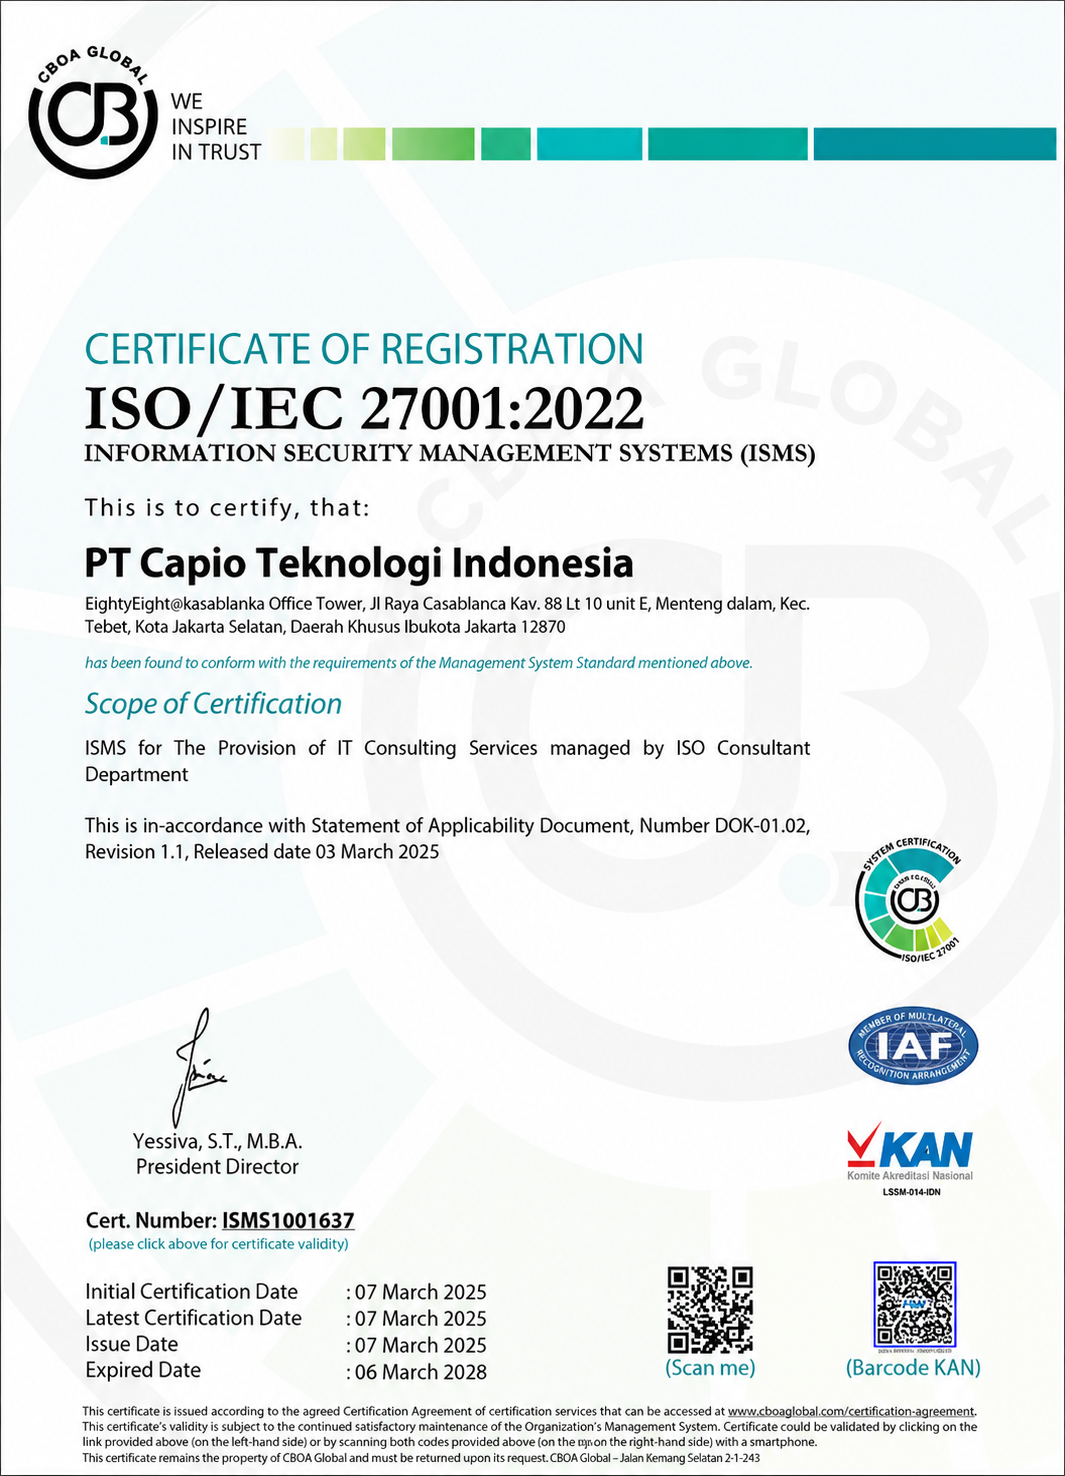
PT Capio Teknologi Indonesia helps regulated organizations secure critical systems, achieve ISO 27001 readiness, close IT audit gaps, and meet OJK, Bank Indonesia, Bappebti, and PDP requirements.
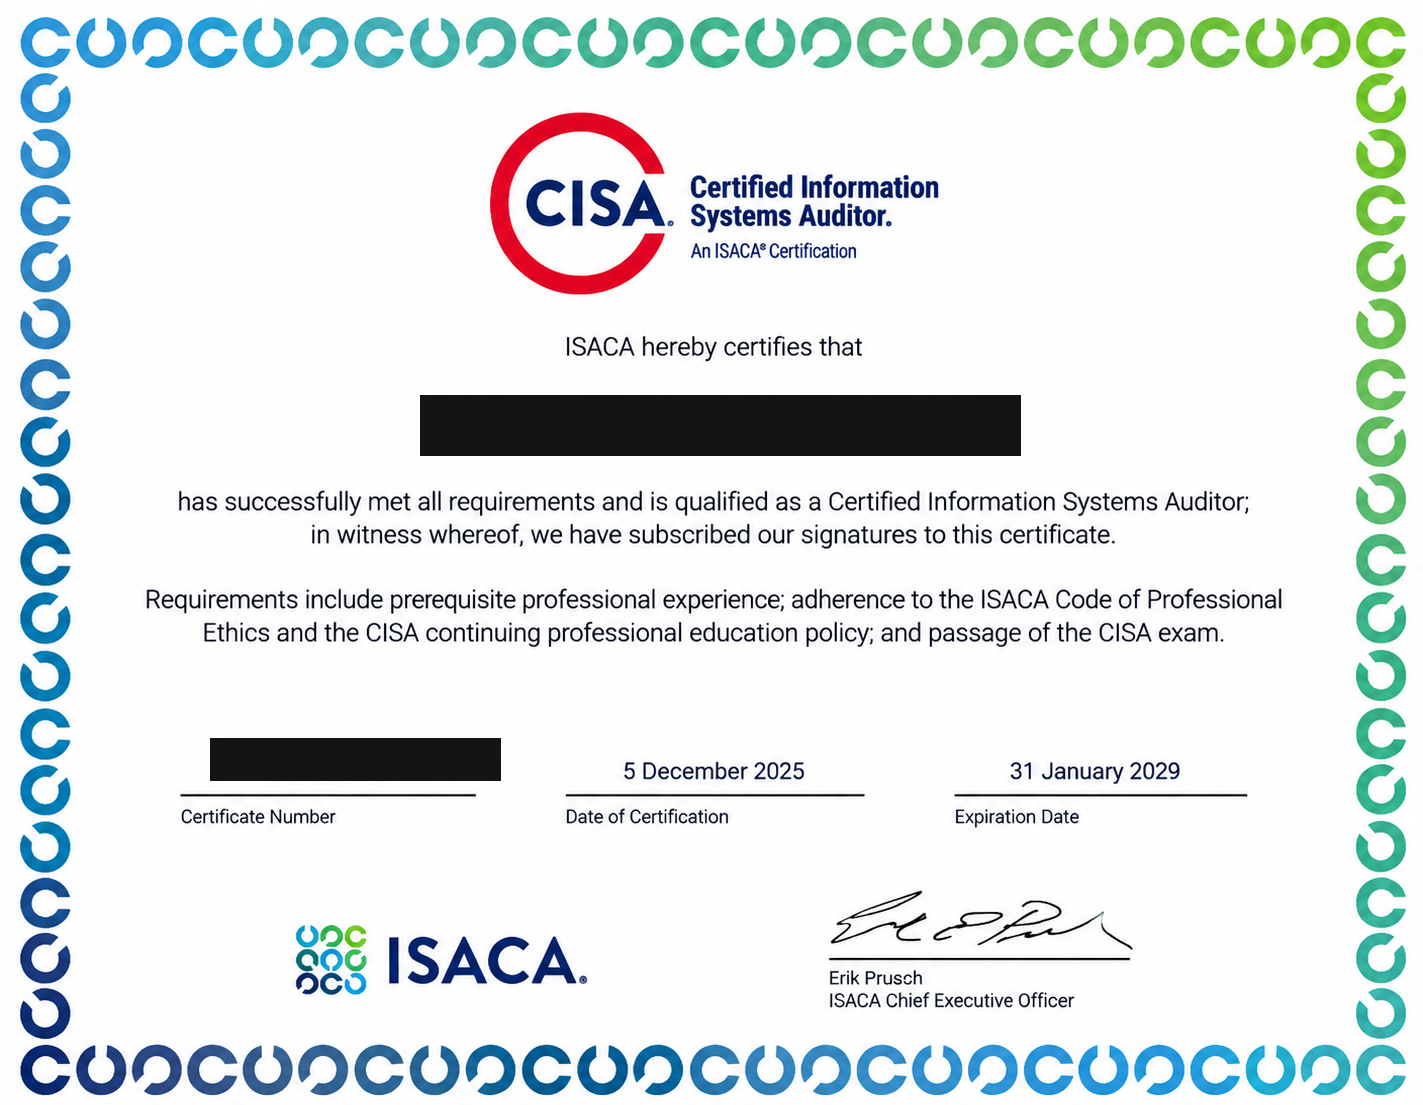
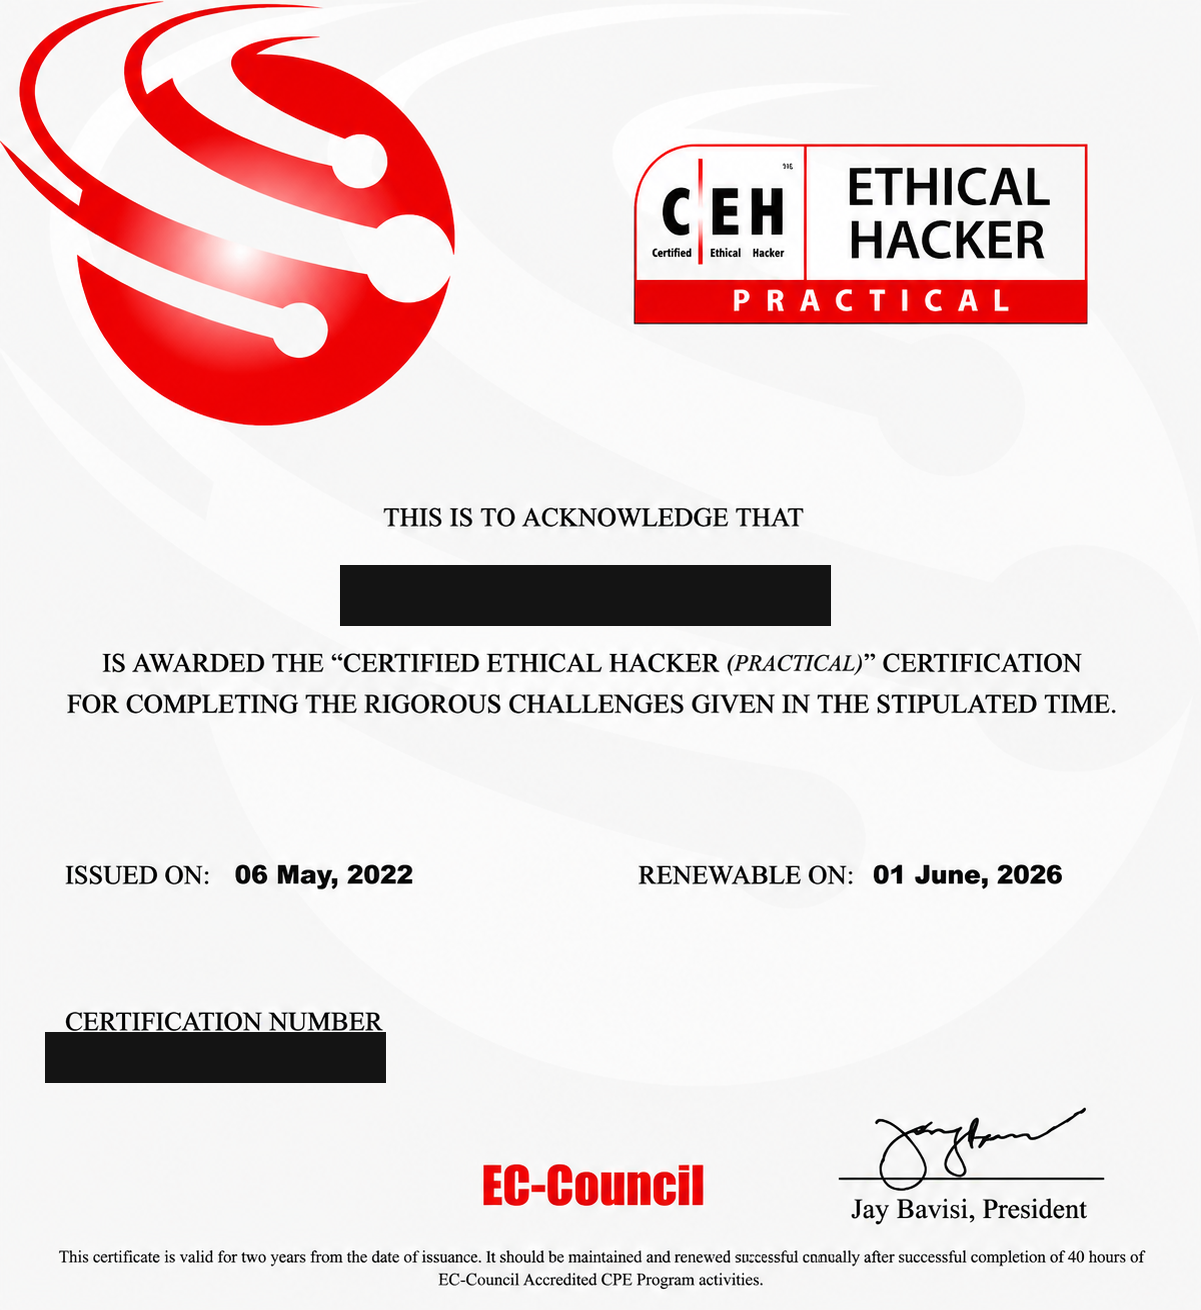
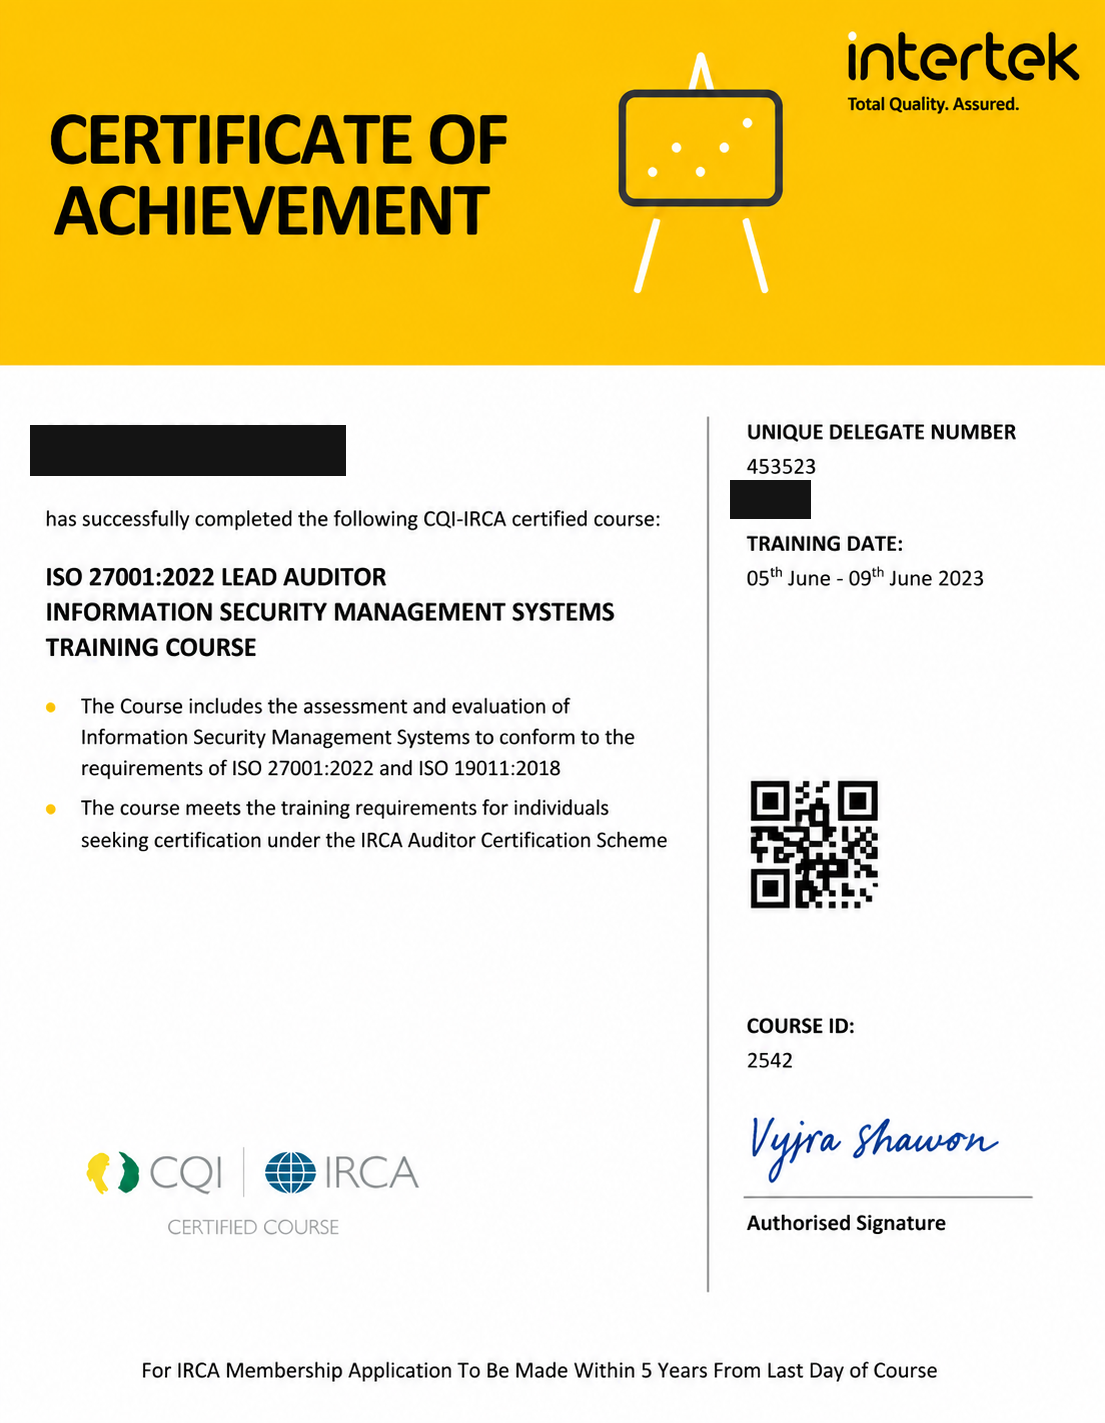
ISO/IEC 27001:2022 · ASPI · CISA · OSCP
Proven in Regulated Environments
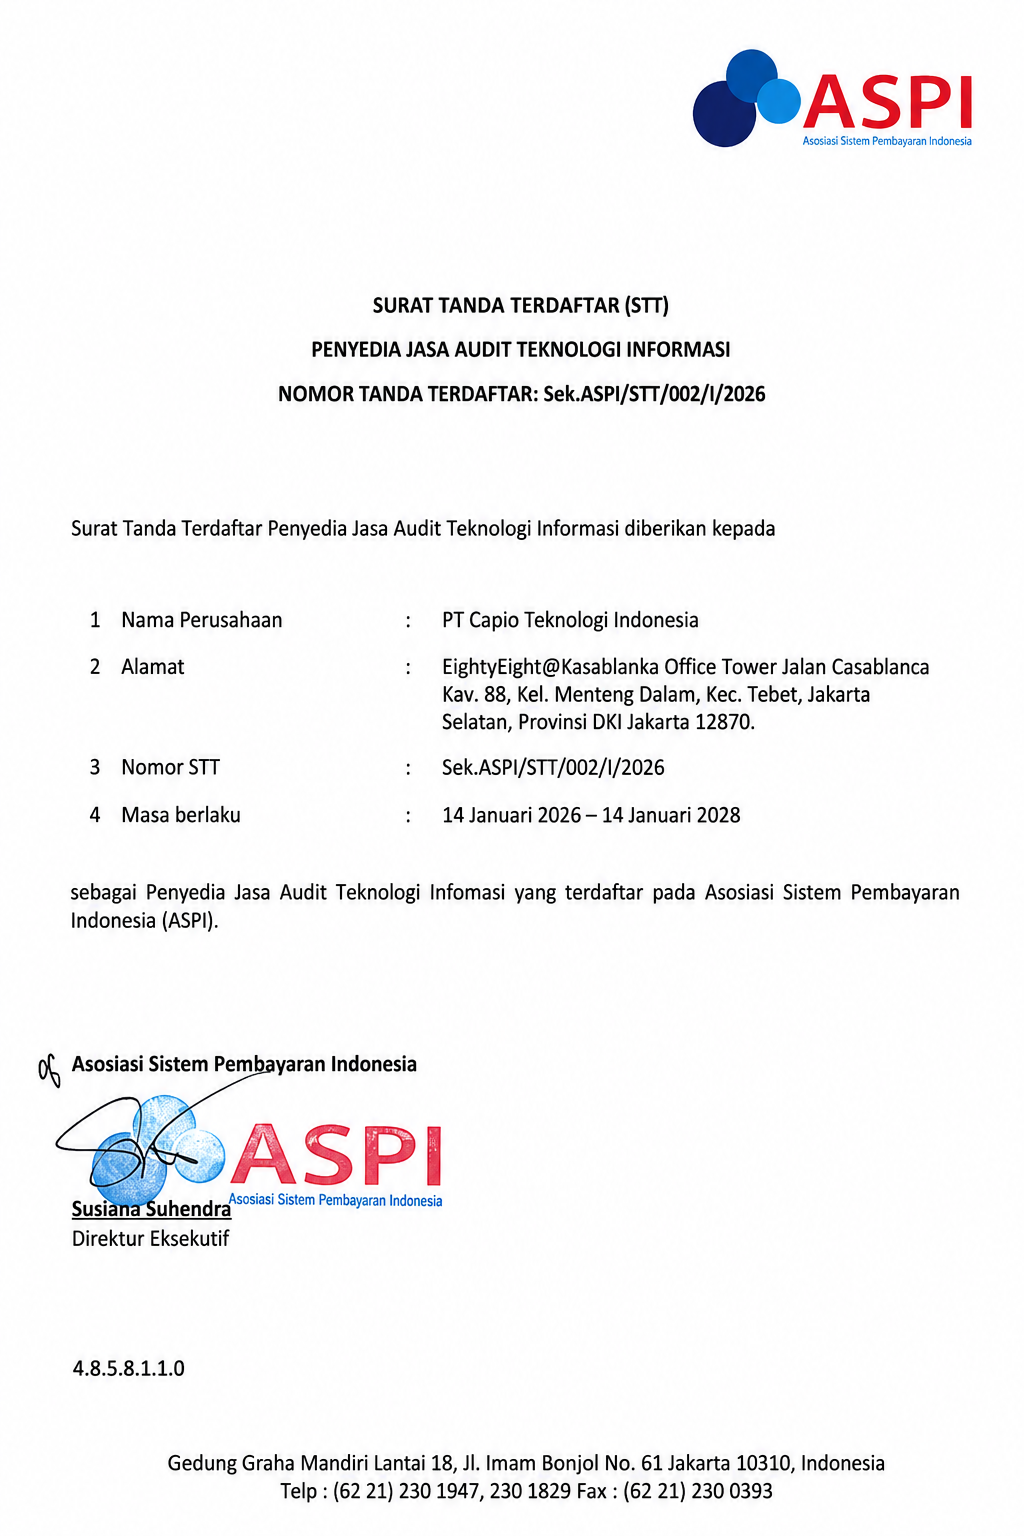
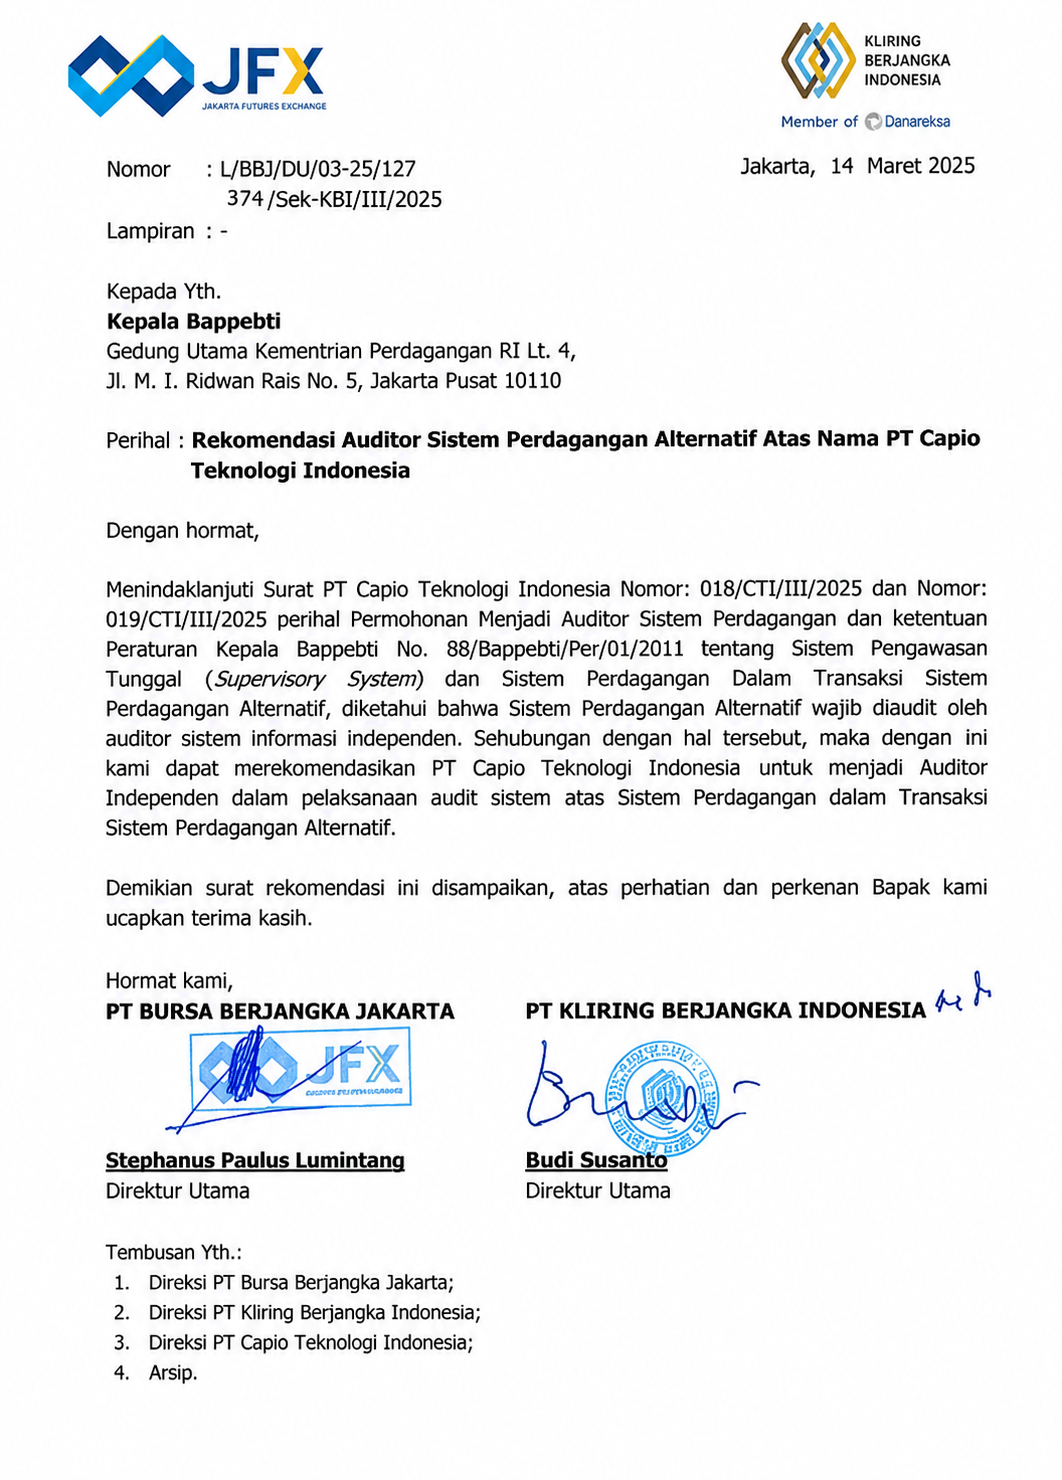
120+ organizations supported, 250+ projects delivered, backed by company credentials and specialist certifications across cybersecurity, IT audit, ISO 27001, and regulatory compliance.
View Proof & CredentialsCompany Credentials
Team Certifications
Selected Clients
Cybersecurity, Compliance & IT Governance
Find weaknesses. Close gaps. Build audit readiness.
Also supporting: Security Awareness · Business Process & SOP · Digital Systems
Built for Indonesia's Regulatory Environment
Cybersecurity, IT governance, audit readiness, and compliance implementation aligned to OJK, Bank Indonesia, Bappebti, PDP, and ISO requirements.
From Requirements to Measurable Readiness
Capio helps regulated organizations move from cybersecurity, audit, and compliance requirements to practical implementation, validated remediation, and regulator-ready evidence — with less rework and clearer accountability.
From Fragmented Controls to Audit-Ready ISO 27001
Structured ISO 27001 readiness from gap assessment to internal audit preparation.
- Gap assessment
- Risk register & ISMS documentation
- Internal audit readiness
Clear controls, accountable ownership, and structured certification readiness.
Find the Risk. Fix the Gap. Verify the Closure.
Security validation focused on exploitable weaknesses, remediation, and retesting.
- Risk-ranked findings
- Remediation guidance
- Retest verification
A prioritized remediation path with agreed findings revalidated before closure.
Turn Audit Findings into Accountable Controls
Governance improvement built around ownership, evidence, and closure.
- Control ownership
- Evidence mapping
- Remediation roadmap
Clear accountability and a management-ready governance roadmap.
Be Audit-Ready Before the Audit Begins
Structure controls and evidence before they become last-minute audit issues.
- Control mapping
- Evidence matrix
- Readiness checklist
Fewer evidence gaps and a more efficient audit preparation process.
Turn Manual Processes into Controlled Digital Workflows
Controlled workflows designed around ownership, access, and implementation discipline.
- Workflow mapping
- Role-based access
- UAT support
A working platform delivered on schedule and ready for controlled adoption.
Turn Security Awareness into Everyday Action
Practical training aligned to phishing, fraud, and social-engineering scenarios.
- Phishing awareness
- Fraud & social engineering
- Employee reporting behavior
Stronger employee response to real-world threats and security controls.
From Gap Identification to Verified Closure
Capio moves each engagement through assessment, design, implementation, validation, remediation, and continuous improvement — helping clients reduce rework and reach audit, security, or compliance readiness more efficiently.
Identify gaps, risks, and regulatory requirements.
Prioritized readiness baseline.
Translate findings into controls, ownership, and a practical roadmap.
Clear implementation plan.
Implement controls, documentation, and agreed remediation.
Operational improvements.
Test whether implemented controls and remediation work as intended.
Evidence and verified results.
Close findings, refine controls, and reduce remaining gaps.
Closure readiness.
Embed governance, repeatable processes, and continuous improvement.
Sustainable security and compliance.
Clear Scope · Practical Remediation · Validation · Closure Focus
Capio stays engaged beyond assessment to support agreed remediation, evidence preparation, and readiness validation.
Planning a Pentest, ISO 27001 Project or IT Audit?
Talk to Capio to define the right scope, required deliverables, and practical next steps.